TRISUL NETWORK ANALYTICS
AI-Assisted NetFlow and Packet Analytics for Deep Network Visibility
Trisul 8.0 is here, now with Trisul AI
Analyze NetFlow, packets, BGP, SNMP, and Syslog in one platform to detect anomalies, investigate incidents faster, and generate audit-ready network data without switching tools.
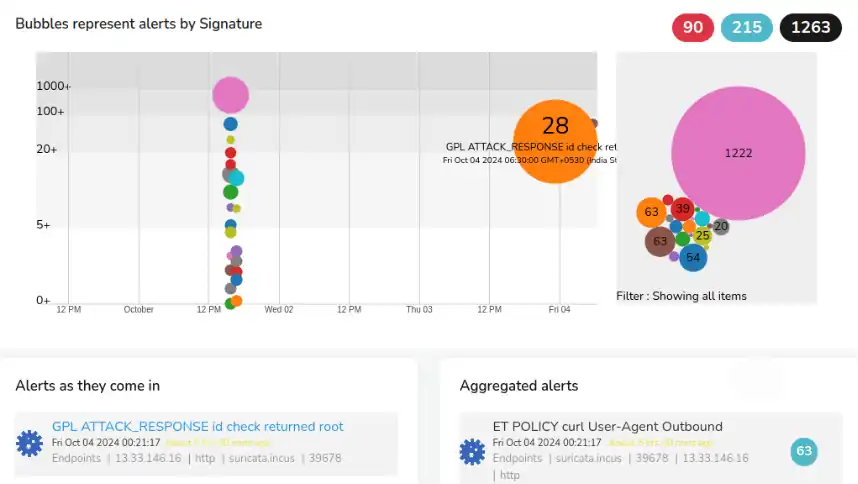
Network Traffic Monitoring for Security & Compliance
For ISPs · Security Teams · Enterprise Networks


Deep Metrics for Real-Time Network Visibility
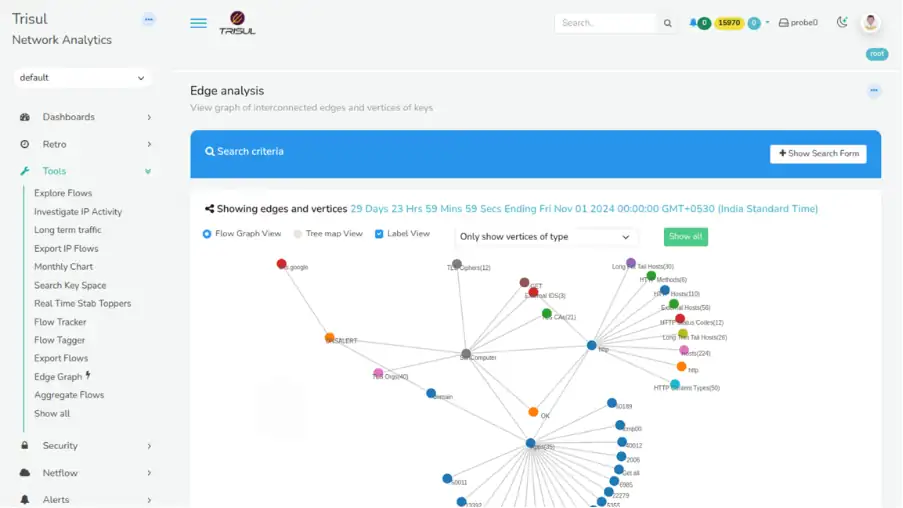
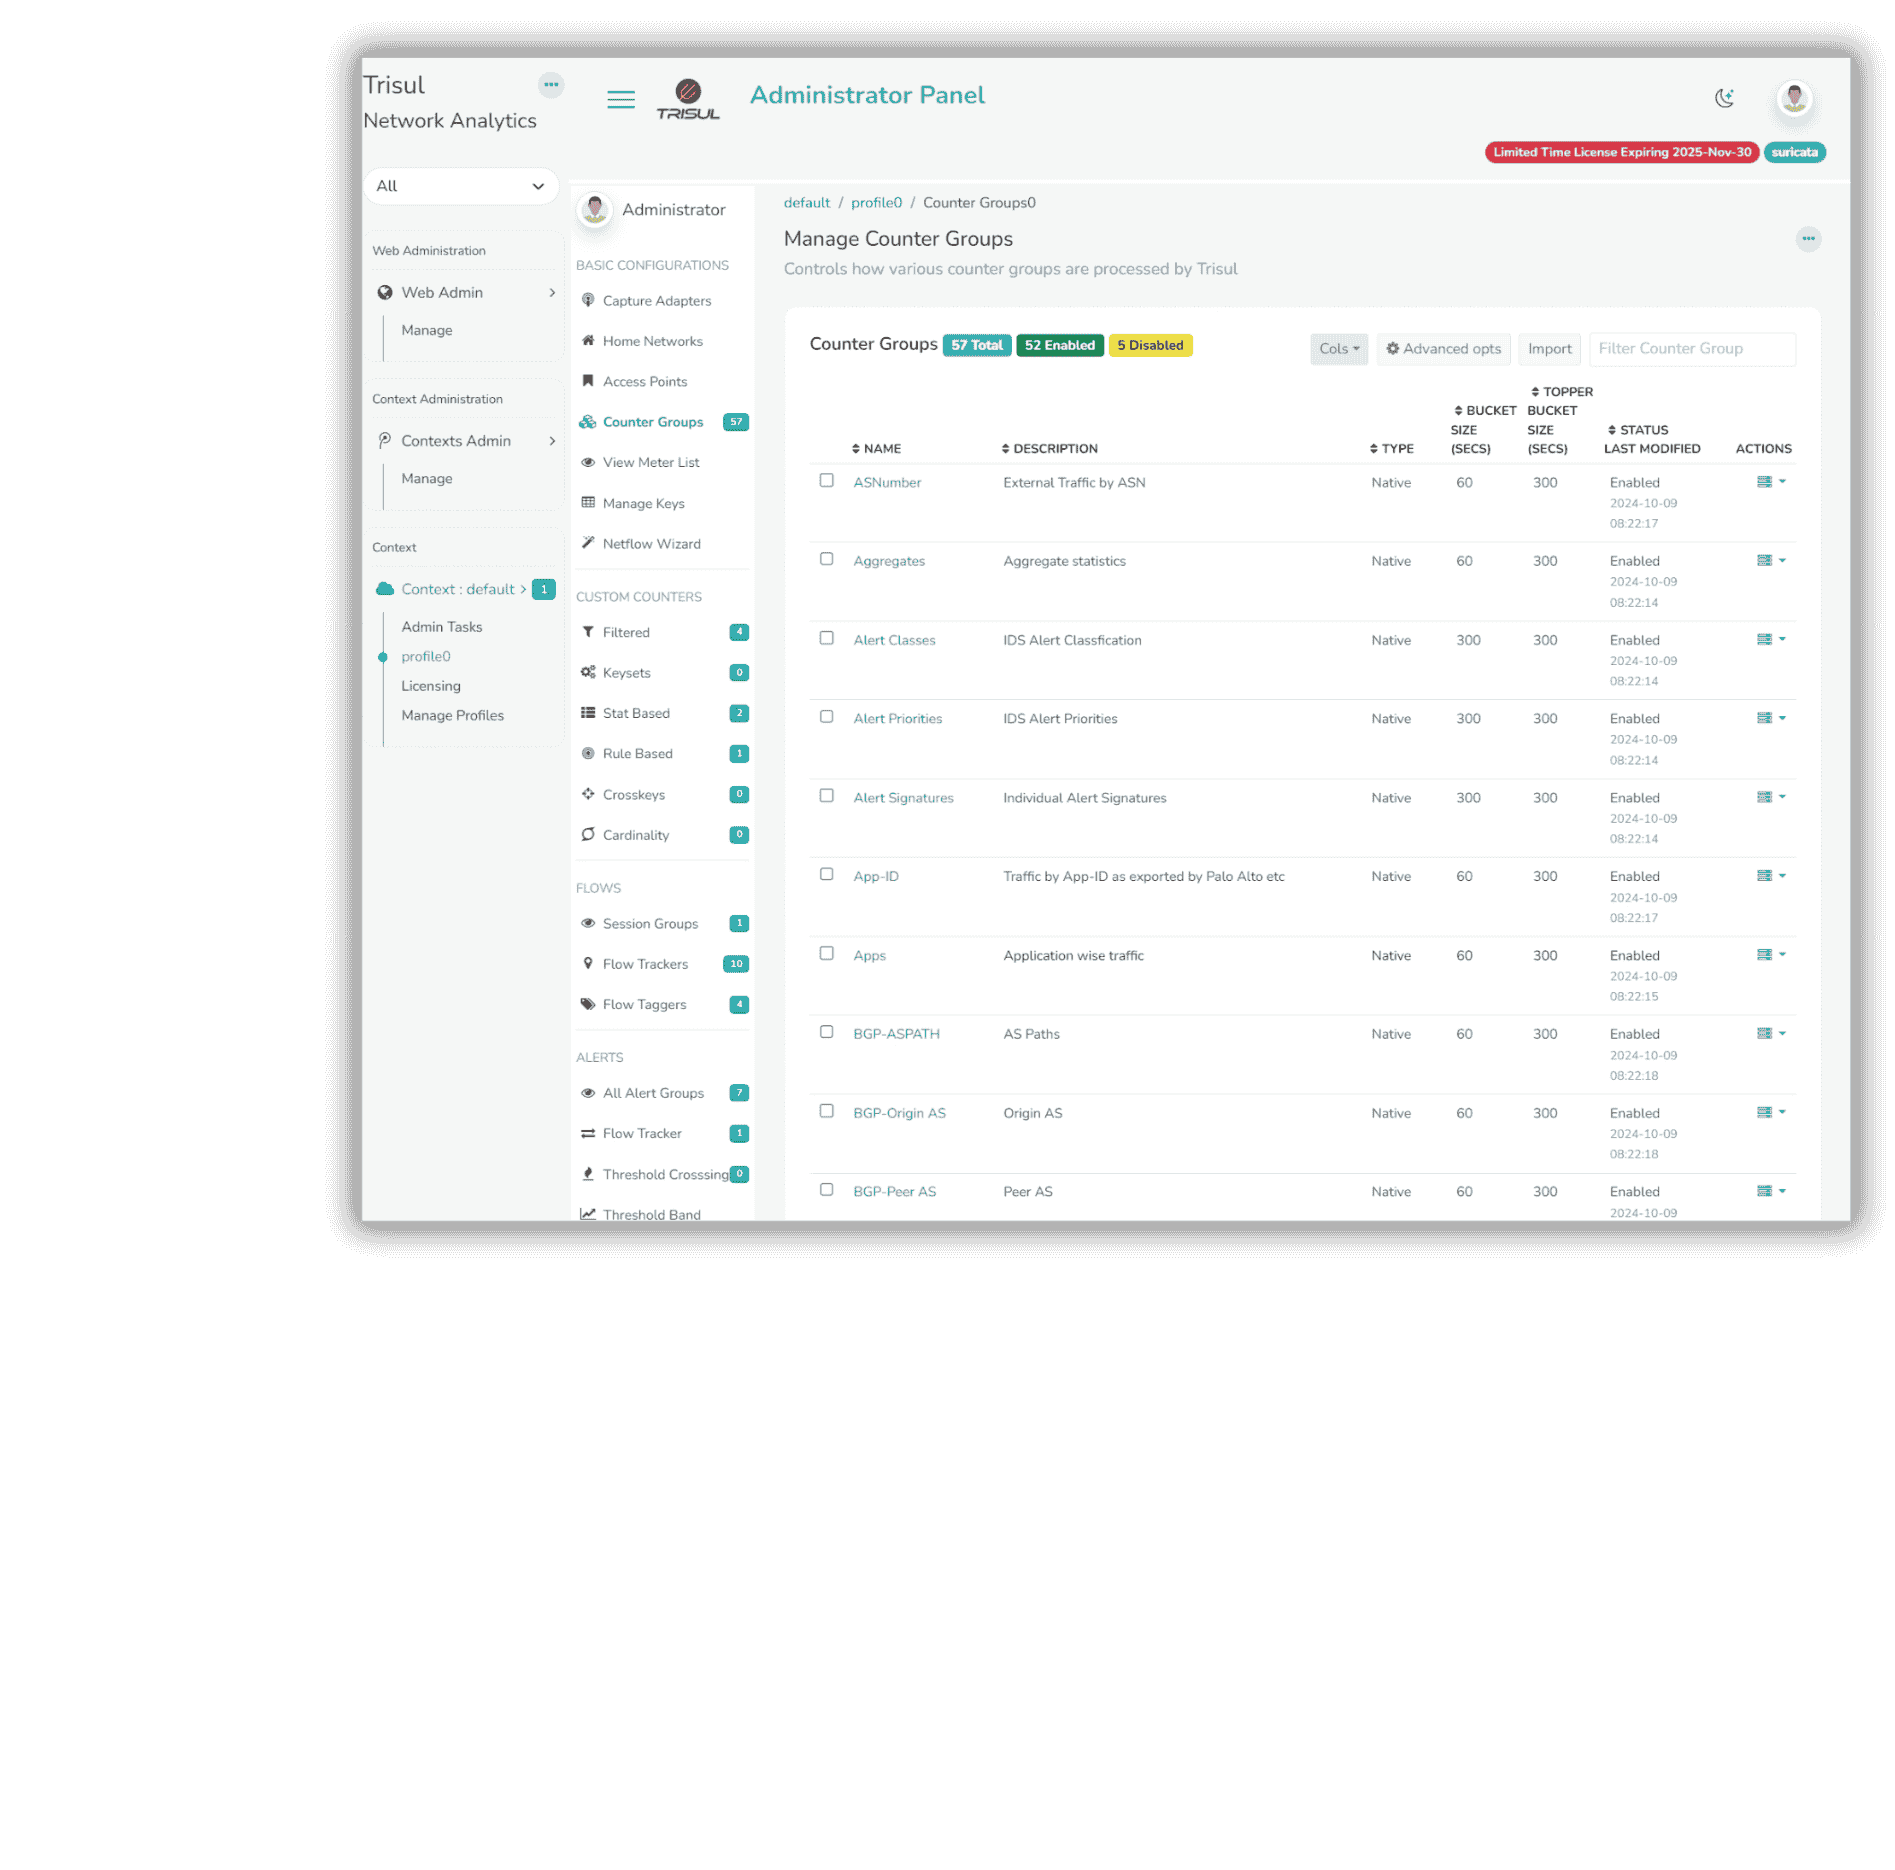
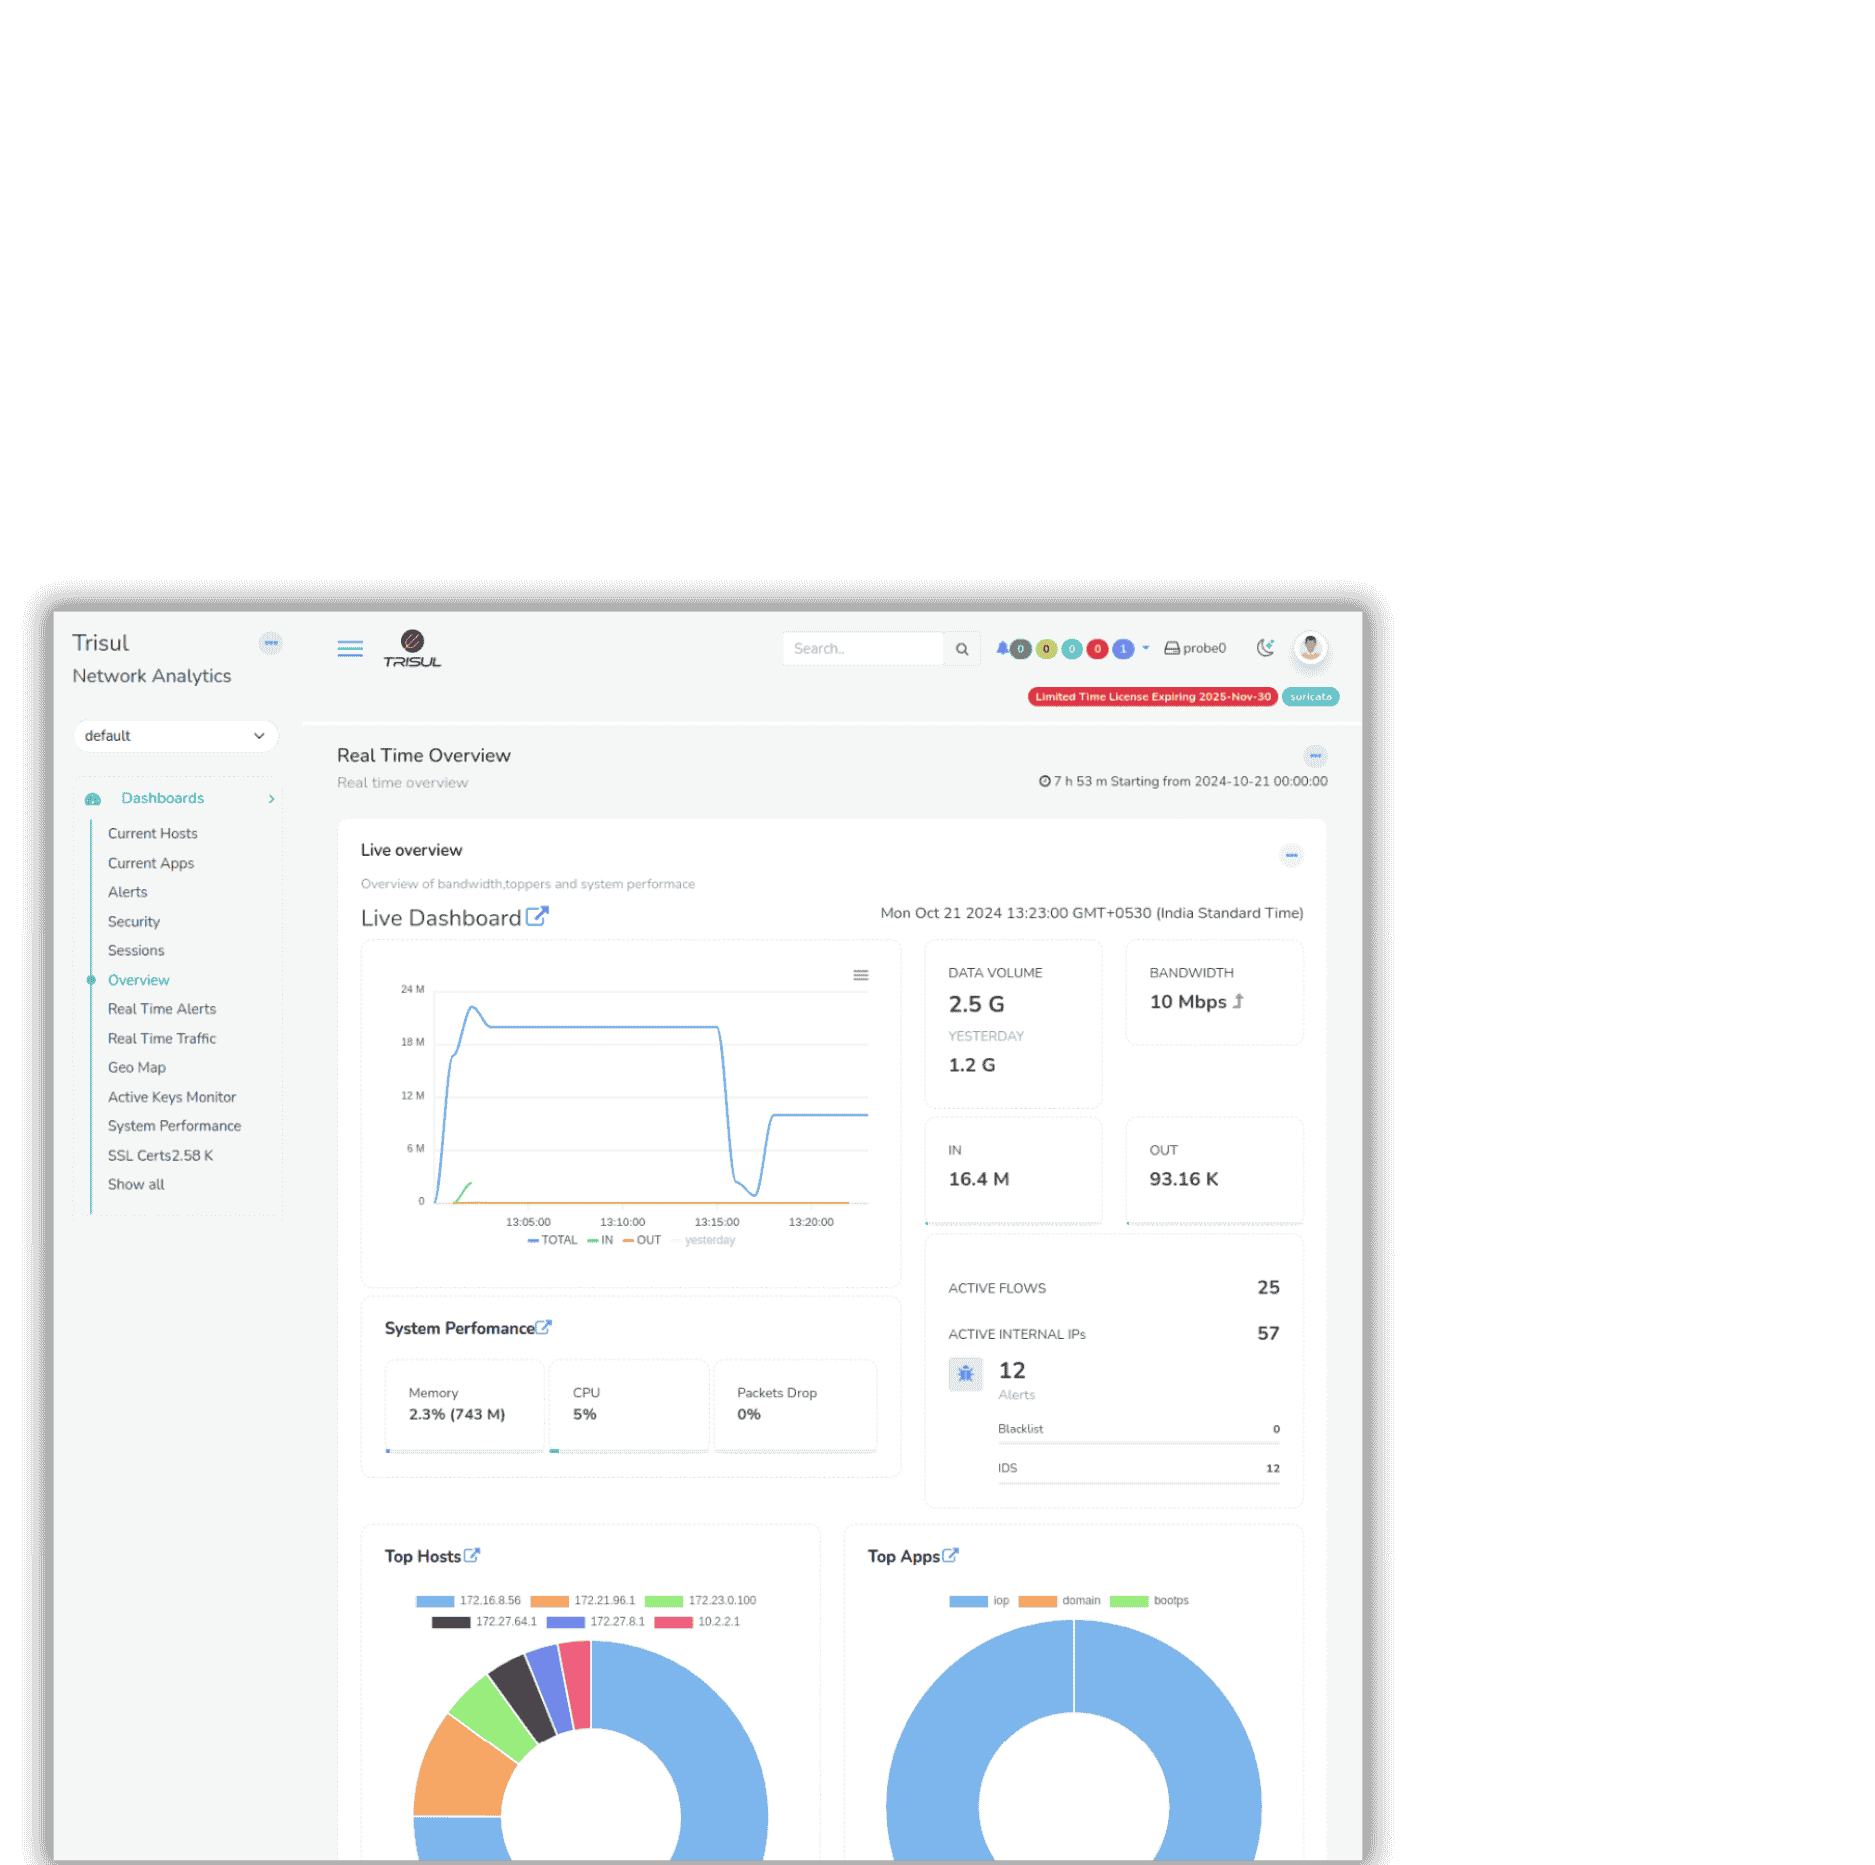
Gain full visibility into network performance with deep metrics across applications, hosts, TLS, Ethernet, and geo data. Combine this with flow analysis and graph-based insights to detect anomalies early and investigate issues in real time.
- Analyze millions of metrics across network, application, and infrastructure layers in real time.
- Built-in algorithms: Top-K, Bottom-K, cardinality, and first-seen detection
- Perform retrospective analysis for faster incident response
- Ingest packets, NetFlow, SNMP, and logs in a single platform
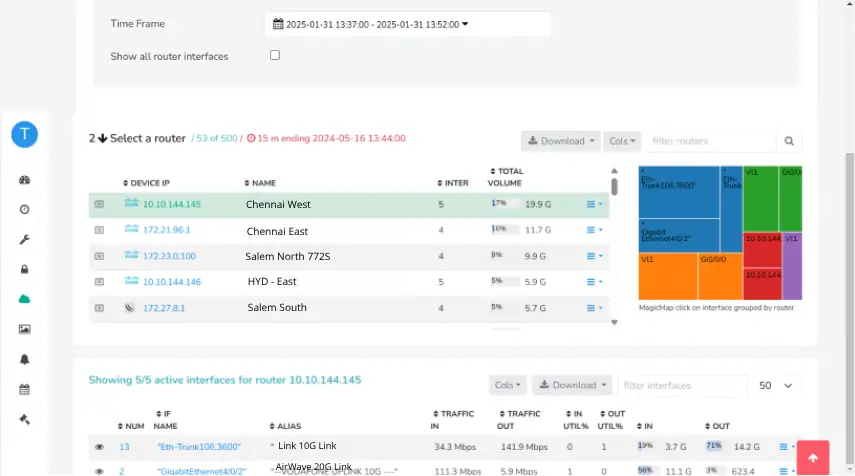
Capture and Analyze Every Network Flow in Real Time
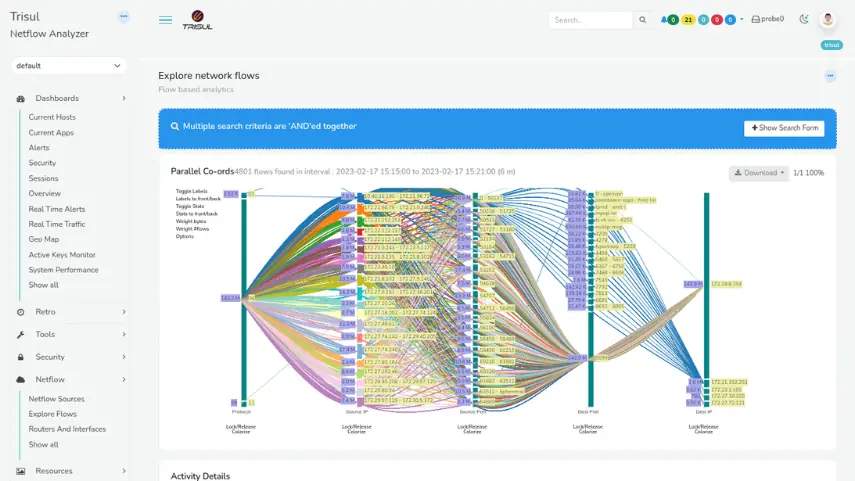
Track every network flow across your infrastructure without sampling, summarization, or data loss. Capture every network flow without sampling to enable accurate investigation and forensics.
- Ingest NetFlow, sFlow, IPFIX, or reconstruct flows directly from packets
- Query flow data with a flexible, high-performance search language
- Add context with Flow Taggers for faster filtering and investigation
- Store complete flow records with no rollups or data reduction
Why Network Teams Choose Trisul for Flow and Packet Analytics
Frequently Asked Questions About Trisul Network Analytics
What is Trisul Network Analytics?
Trisul Network Analytics is a network traffic and security analytics platform from Unleash Networks. It combines NetFlow, packet capture, SNMP, BGP and syslog analysis in one platform, so ISPs, security teams and enterprises can monitor traffic in real time, detect anomalies, investigate incidents and generate audit-ready network records without switching between tools.
What is the difference between flow analysis and packet analysis?
Flow analysis uses summaries of network conversations (NetFlow, sFlow or IPFIX records exported by routers and switches) to show who talked to whom, when and how much. Packet analysis captures the actual traffic, which allows deep inspection, session reconstruction and forensic investigation. Trisul supports both: it can analyze flow records from your routers or build flows directly from captured packets.
What data sources does Trisul support?
Trisul ingests NetFlow, sFlow and IPFIX from routers and switches, raw packets from a SPAN or mirror port, SNMP, syslog and BGP. It can also process large PCAP files for retrospective analysis. Data can be explored in Trisul’s built-in interface, or used from tools like Grafana, Kibana and Splunk through its APIs.
How is Trisul deployed?
Trisul installs as Linux packages on Ubuntu 22.04, 24.04 or 26.04, or on RHEL/Oracle Linux 8, 9 or 10, on a physical server or a virtual machine. The minimum setup is 4 CPU cores, 8 GB RAM and 200 GB of disk. You can start with a single server and scale out with distributed probes and a central hub as your network grows.
Is there a free trial, and how is Trisul priced?
Yes. A free, full-featured 7-day trial license is installed automatically with Trisul, and no credit card is required. The trial supports up to 2 NetFlow routers, 10 GB of packet storage and one probe, and you can request an extension from within the app. Production licenses are perpetual, priced by the number of active internal IPs (up to 500, up to 3,000, or unlimited), and include one year of support. Special pricing is available for ISPs.
Can Trisul help ISPs meet IPDR and DoT compliance requirements?
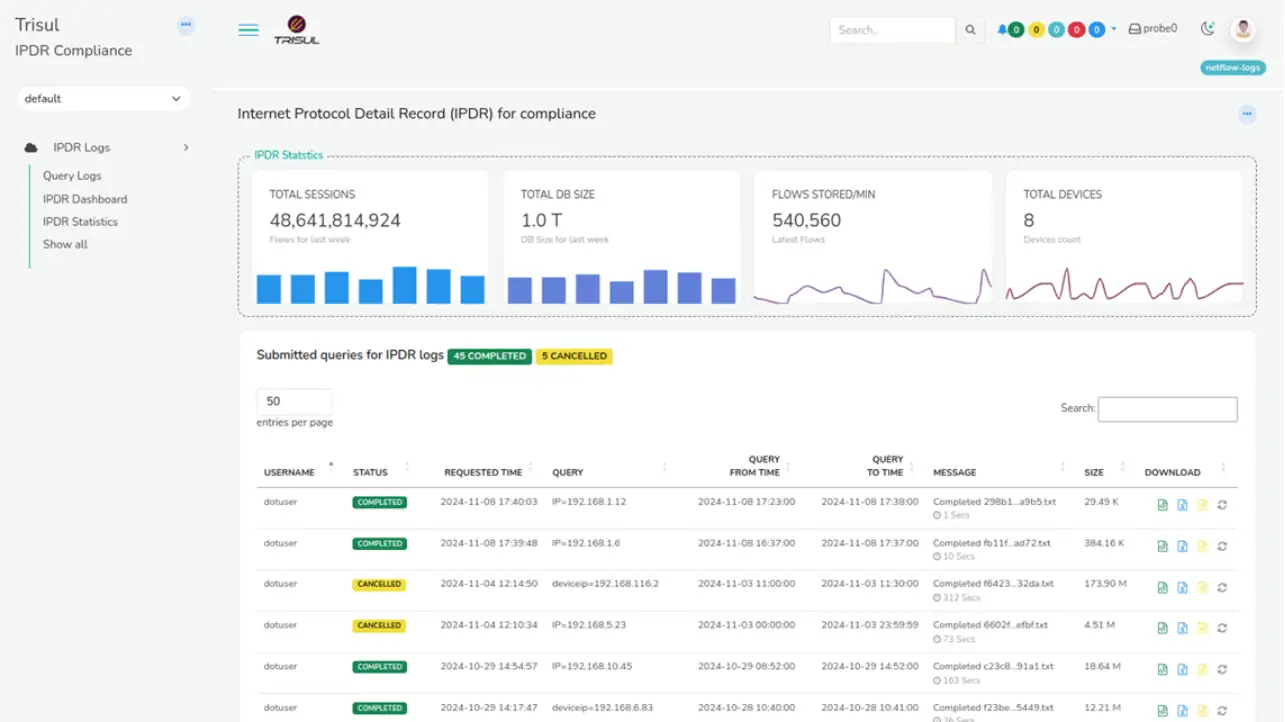
Yes. Trisul IPDR stores the flow records required for India’s Department of Telecommunications (DoT) IPDR mandate, including timestamps, source and destination IPs and ports, post-NAT addresses, and user IDs from AAA logs. It supports IPv4 and IPv6, compresses records to reduce storage costs, and includes a self-service portal where authorized agencies can query and download logs, with every query recorded for audit. ISPs in other countries can use it to keep complete IP flow logs too.
Start Monitoring Network Traffic in Minutes
Try Trisul with a full-featured three– day 7-day trial. Analyze NetFlow, packets, and PCAP data in real time without sampling or limitations. Deploy instantly using our Docker image on Linux and start gaining complete network visibility.
No Credit Card Required.